
On 18 November 2025, the European authorities EBA, ESMA and EIOPA published the first list of ICT service providers considered “critical” within the meaning of the Digital Operational Resilience Act. Behind this regulatory move lies a real strategic diagnosis. For the first time, Europe sets out in black and white the technological dependencies that condition the resilience of its financial system.
This list, which places nineteen providers under the direct supervision of a European “Lead Overseer”, marks a new era: one where technology providers become fully regulated actors, on the same footing as financial institutions. Strengthened audits, mandatory testing, information requests, remediation plans and increased transparency are now imposed on these giants, whose failure could disrupt the financial stability of the Union.
For banks, insurers, OPCAs, market infrastructures and fintechs, DORA does not change the obligations already in force, but it changes the operational reality. Critical providers must absorb new constraints, revise their SLAs, adjust their support models and sometimes even pass on compliance costs. Organisations will therefore need to rethink their risk analyses, continuity plans, cloud strategies and contractual relationships.
A list that reveals without filter the true digital architecture of Europe
The list published by the Commission includes the following actors: Accenture, Amazon Web Services, Bloomberg, Capgemini, Colt, Deutsche Telekom, Equinix, FIS, Google Cloud, IBM, InterXion, Kyndryl, LSEG Data and Risk, Microsoft Ireland, NTT Data, Oracle, Orange, SAP and Tata Consultancy Services.
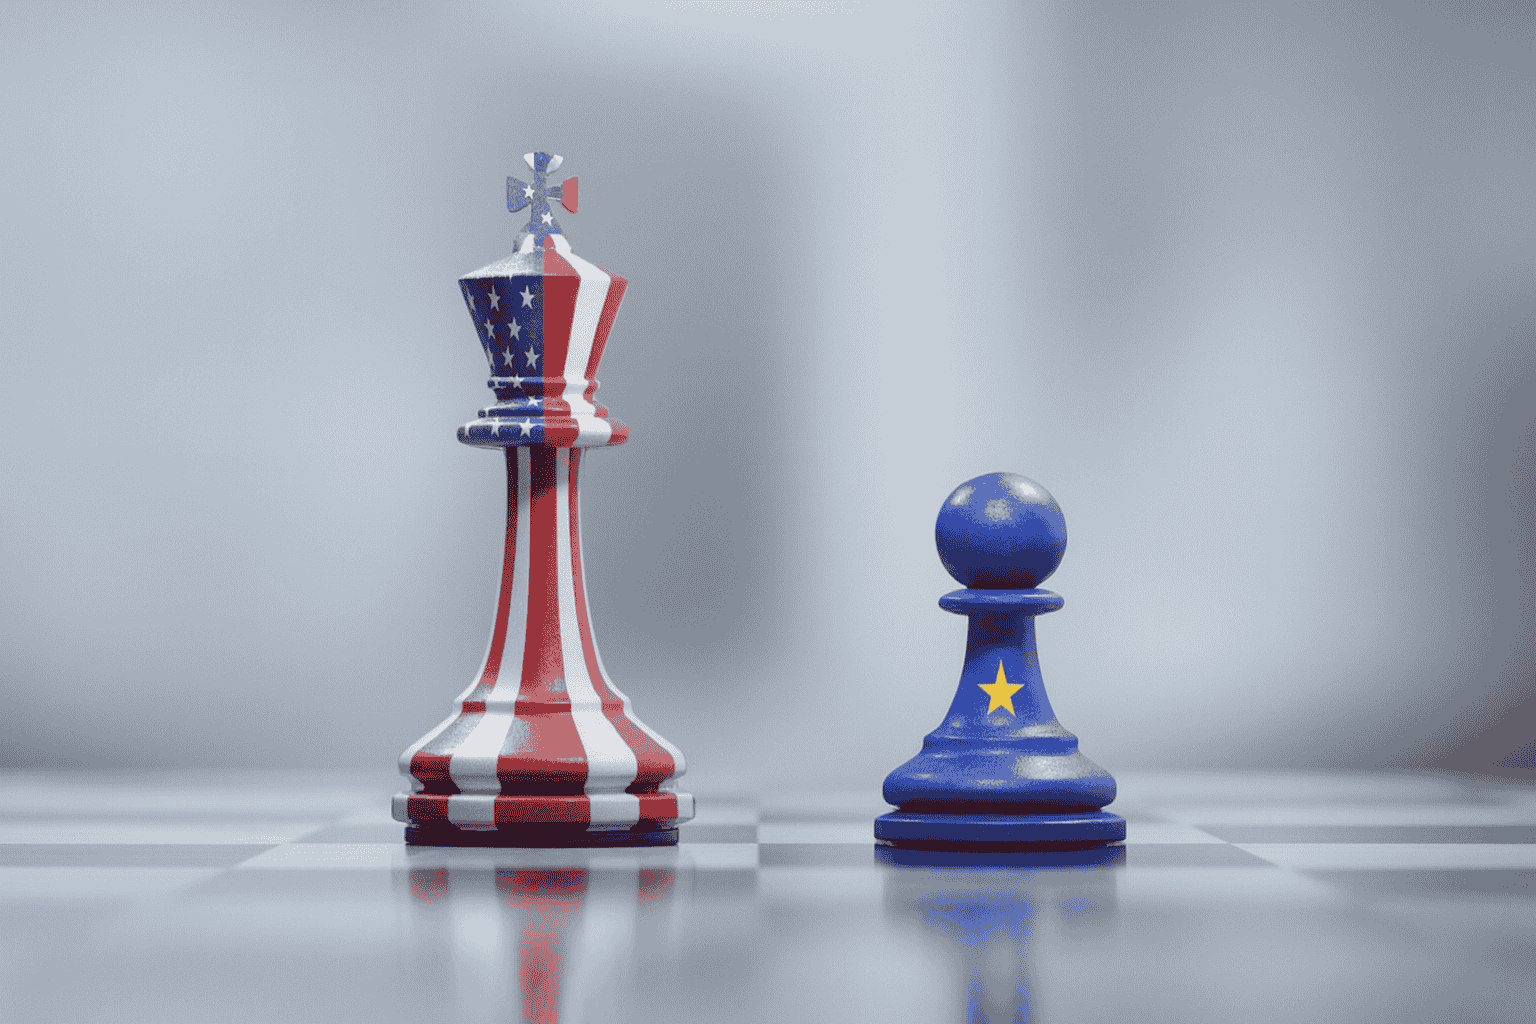
This official mapping sheds light on a truth long known but rarely acknowledged publicly: the resilience of the European financial sector relies largely on American actors. Neither sovereign cloud, nor European cybersecurity initiatives, nor local operators have, so far, managed to build an ecosystem capable of competing with the power of the hyperscalers.
American hyperscalers: a monopoly built by US public procurement
Behind the dominance of AWS, Microsoft and Google lies an element often omitted in European debates: these actors were propelled by US public procurement. The federal government massively invested in their infrastructures, providing them the volumes, financial resources and credibility needed to then win over the world.
To this public support is added a far more powerful and risk-tolerant American financial ecosystem, where massive fundraising rounds, long investment cycles and ambitious industrial bets are made possible by the depth of venture capital, the liquidity of the markets and a culture of hypergrowth.
These conditions, structurally more favourable than in Europe, enabled the hyperscalers to finance colossal infrastructure capacities for more than a decade, long before they became profitable.
Where the United States built the dominance of its hyperscalers by feeding them through federal public procurement and defence programmes, France did not choose a digital “Buy French”, nor even a structured “Buy European” approach. Germany is beginning to use its public purchasing more actively to support its industrial sectors, particularly in cloud and cybersecurity, whereas France remains confined to an apparent neutrality of markets. Result: faced with unfair or asymmetric international competition, our national champions remain undersized compared to the potential of public procurement, while American giants are overrepresented in major contracts of the State, public operators and local authorities.
This reality changes the reading of DORA. Europe is merely acknowledging a technological dependency born elsewhere, shaped by a foreign industrial strategy. It is now trying to compensate for the absence of its own industrial policy through a supervisory framework. Having failed to build its own champions, it regulates those of others.
A new dynamic: geopatronage settles into the European landscape
Behind the DORA list emerges another decisive phenomenon: geopatronage. According to Gartner, it will be one of the major technological trends of 2026. European companies, after two decades of migration towards global clouds, are beginning to repatriate their data and applications to sovereign or local solutions.
This movement, born in sovereign sectors, is now spreading to local authorities, semi-public operators, mutual insurers, hospitals and also private actors. The issue no longer stops at GDPR compliance: it is about regaining control over data, contracts, costs, customer relationships and service stability.
The wave of acquisitions of French providers by US groups feeds this sensitivity. Many organisations now seek European solutions capable of guaranteeing local support, pricing control and contractual frameworks under French law.
Critical infrastructures: an invisible but decisive dependency
American actors Equinix and InterXion as well as major European telecom operators form the overlooked backbone of the digital world. They host core applications, structure interconnections and concentrate the data flows of the financial sector. Their designation as critical providers finally recognises their strategic role.
Only Orange and Deutsche Telekom embody a truly European capability in this category. The other actors, mostly American, provide the physical infrastructures on which banks, insurers, payment platforms and financial markets depend.
These dependencies are also vulnerabilities. The incidents of 2024 and 2025 made this abundantly clear:
- the Snowflake breach, which exposed sensitive customer data worldwide;
- the CrowdStrike outage, which paralysed public services, airlines, hospitals, and other critical sectors;
- and most notably the Cloudflare outage in the autumn of 2025, which rendered thousands of services across Europe inaccessible for several hours, including banks, public portals, SaaS platforms, IAM connectors, and security solutions.
Critical software and financial data: another dependency zone
SAP, Oracle, Bloomberg, FIS and LSEG control most transactional systems, market data, banking ERPs and critical processing chains. SAP symbolises Europe’s capacity to produce world-class software solutions, but it remains an exception. The rest of the ecosystem is dominated by non-European actors.
IT outsourcing and consulting: a strategic power often underestimated
Accenture, Kyndryl, Tata Consultancy Services, NTT Data and to a lesser extent Capgemini ensure a large part of the integrations, transformations, cloud migrations and operations of financial information systems. Their footprint on strategic projects is immense. Dependency is not only technological; it is also organisational.
A sovereignty challenge: Europe must regain control
Only three European providers appear among the nineteen critical actors: SAP, Orange and Capgemini. And none of them operates a hyperscale cloud capable of competing with AWS, Azure or Google Cloud. European sovereignty therefore remains fragmented, concentrated on a few isolated building blocks.
Faced with this observation, Europe is developing an unprecedented tool: the cloud sovereignty score. This framework finally makes it possible to objectively assess the sovereignty level of a provider. Its adoption by public and private organisations is gradually transforming the market. In the long term, it could become a mandatory criterion in tenders, accelerating the geopatronage already underway.
Consequences for financial institutions: a new strategic, not only regulatory, framework
DORA imposes a profound transformation of governance: asset mapping, identification of critical dependencies, ICT risk management, formalisation of security policies, reinforced third-party supervision, strict incident notification and regular resilience testing.
Integrating sovereignty into this governance becomes a major lever. Organisations that understand that resilience goes beyond compliance can turn DORA into a competitive advantage: better contractual control, reduced concentration risk, improved operational oversight, strengthened trust with clients and partners.
Towards a hybrid model: pragmatic sovereignty
The market is evolving towards a hybrid model: part of the uses will remain dependent on hyperscalers for lack of alternatives. But the growth of sovereign, French and European solutions becomes an essential pillar for critical, sensitive or strategic components. Sovereignty ceases to be an absolute; it becomes an architecture.
A Europe that regulates while waiting to rebuild its digital power?
The publication of the DORA list is a political act as much as a regulatory one. It shows where vulnerabilities lie, where systemic risks concentrate and where Europe must invest to regain strategic autonomy.
In the meantime, it chooses to regulate what it cannot yet replace. For executive committees, the question is no longer whether their organisation depends on these critical providers, but how to govern this dependency, anticipate it and integrate it into their resilience strategy.
DORA does not reduce dependency. It reveals it and invites Europe to gradually regain control over its digital destiny.
Share:


