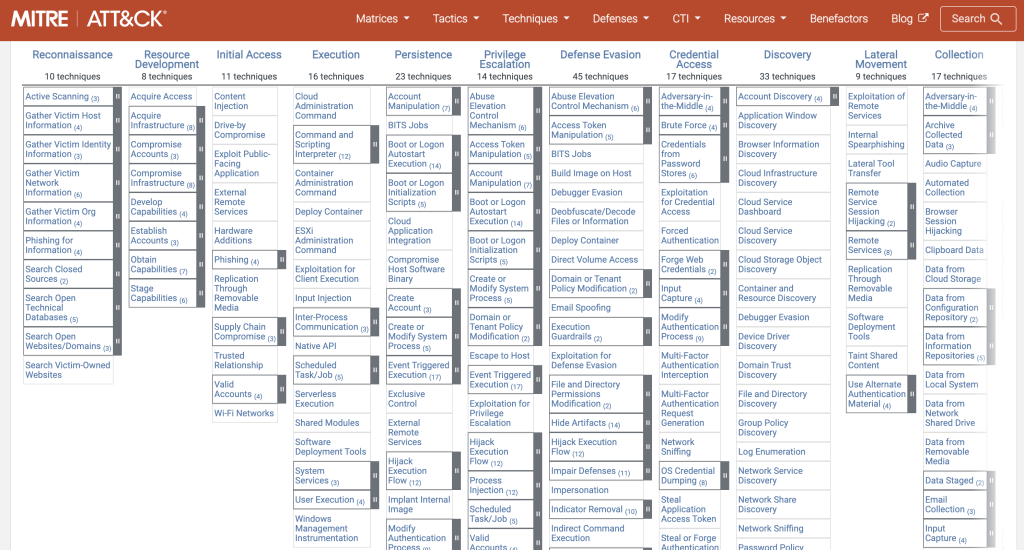
MITRE ATT&CK v17: What to Remember from the New Version

MITRE ATT&CK v17: What to Remember from the New Version

The MITRE ATT&CK framework continues to evolve to stay aligned with real-world threats. Version 17, released in April 2025, marks a major strategic step forward.

This update strengthens coverage for Enterprise, Mobile, and ICS. It refines knowledge structuring, improves technical precision, and incorporates new threat types that had been underrepresented until now.

Here’s what you need to remember.

data breach

Enhanced Attack Mapping

VMware ESXi Hypervisors: An Explicit Target

For the first time, MITRE ATT&CK adds a platform dedicated to VMware ESXi environments.
With ransomware increasingly targeting hypervisors directly, this change was essential. Three new techniques bolster this coverage:

  • Hypervisor CLI

  • ESXi Administration Command

  • Virtual Machine Discovery

Practically speaking, this allows better modeling of attacks seen recently against private cloud infrastructures (e.g., campaigns targeting ESXiArgs, LockBit on ESXi).

Greater Precision in Mitigations

Enterprise mitigations have been reworked to be more actionable. The goal is clear: make integration into defense plans and Zero Trust frameworks easier.
Example: mitigations against hijacking execution flow are now aligned with post-exploitation hardening best practices.

Clarification on Network Devices

The platform formerly called “Network” becomes “Network Devices.”
Objective: remove ambiguity—only attacks against equipment such as switches, routers, and firewalls are covered, not general network traffic.

Rationalization and Technique Mergers

Several redundant or ambiguous techniques were consolidated to improve clarity:

  • Hijack Execution Flow: DLL Side-Loading is now merged with Hijack Execution Flow: DLL.

  • DLL Search Order Hijacking was also renamed to reflect these changes.

These mergers prevent confusion between closely related but technically distinct DLL injection methods.

By MITRE Domain: What Changes

Enterprise Domain

  • 14 tactics, 211 techniques, 468 sub-techniques, 755 software referenced.

  • New techniques:

    • Obfuscated Files or Information: SVG Smuggling

    • Obfuscated Files or Information: Junk Code Insertion

    • Masquerading: Overwrite Process Arguments

    • Trusted Developer Utilities Proxy Execution: JamPlus

  • Scope expanded:

    • Software Extensions: IDE Extensions

    • User Execution: Malicious Copy and Paste

    • Email Bombing and Email Spoofing added as standalone techniques.

Mobile Domain

  • 12 tactics, 75 techniques, 46 sub-techniques, 118 software.

  • Added:

    • Virtualization Solution (techniques related to mobile virtualization solutions)

    • Major update to SIM Card Swap 2.0.

ICS (Industrial Control Systems) Domain

  • 12 tactics, 83 techniques, 0 sub-techniques, 23 software.

  • Patches and adjustments:

    • Alarm Suppression, Manipulate I/O Image, Rootkit.

  • Newly identified threat:

    • FrostyGoop, a specialized industrial malware.

Focus on Added Threat Actors and Malware

Threat Groups (APTs) Added

  • APT42 (Iran): espionage in the Middle East.

  • RedEcho (China): campaigns against Indian critical infrastructure.

  • Sea Turtle: hijacking of critical DNS infrastructure.

  • Velvet Ant and Salt Typhoon: groups recently tied to supply-chain attacks.

Recent Software and Malware

  • LightSpy (advanced mobile surveillance).

  • StrelaStealer (credential theft).

  • ShrinkLocker (ransomware targeting the banking sector).

  • Kapeka (modular implant).

  • BlackByte 2.0, LockBit 3.0, Akira v2 illustrating the growing sophistication of modern ransomware.

Our Takeaways

MITRE ATT&CK v17 doesn’t just document more techniques. It structures the threat landscape as it unfolds today:

  • Attacks against hypervisors
  • Extreme obfuscation
  • Abuse of user behavior
  • The rise of social engineering and hybrid vectors

For SOCs, CTI analysts, and architects, this evolution is essential to align detection, hunting, and response with actual adversary methods.

Official Resources

Share:

X
LinkedIn