Skip to content
Stroople
  • About us
    • What we lived by
    • Our offices
  • Cybersecurity Services
    • Offensive Security
    • Managed Cyber Defense
      • External Attack Surface Management
      • Threat Exposure Management
      • Managed SOC & CERT 24/7
    • Cyber Advisory & GRC
      • CISO As A Service
      • Cyber crisis management
      • ICT Third-Party Risk Management
      • Regulatory Compliance
    • Training
      • Cybersecurity Training Programme | DORA Compliant
      • Cybersecurity Training Programme | NIS2 Compliant
      • Cyber Crisis Exercise: Immersive Training for COMEX and CIO
  • Careers
  • Resources
    • Blog
    • Cyber Talk
    • Cyber Threat Intelligence
    • Press Releases
  • Contact
    • Change language to Français

Category: GRC

Governance, risk and compliance cybersecurity insights — NIS2, DORA, ISO 27001 and EBIOS RM. Practical guidance, audits and regulatory frameworks to help organizations build a resilient compliance posture.

November 15, 2025November 15, 2025GRC

The Strategic Library for CISO – 12 Essential Books

In a role where every decision can shift a crisis, where every weak signal can become a breach, and where every board […]

November 14, 2025November 14, 2025GRC

Cognitive Security: A New Risk Surface for Organizations

NATO’s recent report on cognitive security (Responding to Cognitive Security Challenges) highlights a shift in the threat landscape: attacks no longer target […]

October 18, 2025October 19, 2025GRC

The Gods of the Cyber-Pantheon: Modern Myths and Digital Punishments

From the Titans of the Cloud to the anti-Cassandras, six modern myths reveal the same original sin: believing that technology protects us […]
September 20, 2025September 25, 2025GRC

European Regulation: Balancing Costs, Compliance, and Competitiveness

You are a business leader. Your audit committee is asking for a clear roadmap to 2026, your CIO is demanding increased investments, […]
Quantas Data Breach
September 8, 2025June 2, 2026GRC

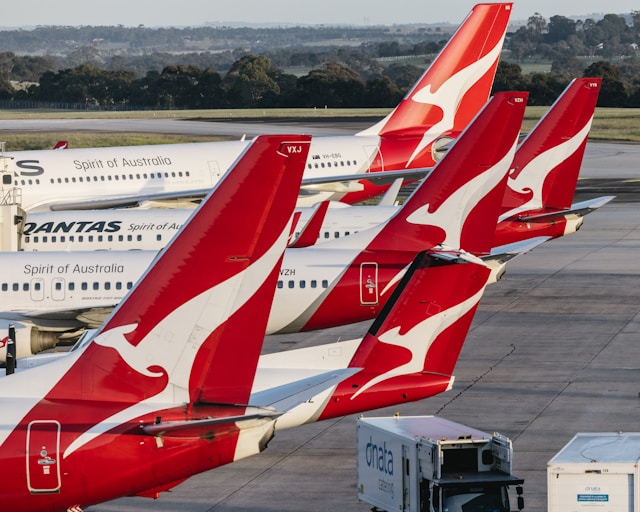
Qantas Cyberattack: 5.7M Customers Exposed, €313K in Executive Bonuses Slashed

When a data breach hits 5.7 million customers and shakes corporate governance, even the boardroom feels the impact. On June 30, 2025, […]

April 10, 2025August 22, 2025GRC

Five Key Lessons from DORA for ICT Providers

Turning regulatory constraint into strategic advantage The introduction of the European Digital Operational Resilience Act (DORA) marks a major shift for ICT […]

June 23, 2024August 16, 2026GRC

How to achieve DORA compliance?

Lockbit: from Genesis to the Last Judgment How to Achieve DORA Compliance? A Guide for Cybersecurity Professionals Scroll Down In the financial […]

April 30, 2024May 23, 2026GRC

5 questions CISOs should ask before taking a new job

5 questions CISOs should ask before taking a new job 5 questions CISOs should ask before taking a new job Scroll Down […]
February 7, 2024July 26, 2024GRC

NIST CSF vs. ISO 27001

NIST CSF vs ISO 27001 NIST CSF vs. ISO 27001 Which Compliance Standard Should You Choose? Scroll Down ISO 27001 and NIST […]
January 14, 2024March 25, 2025GRC

Cyber Insurance : reduced coverage for increased costs.

Cyber Insurance Reduced coverage for increased costs Scroll Down With the rise of cyber threats, organizations are now encouraged to invest in […]

Posts pagination

< 1 2 3 >

Proudly Powered by WordPress

Company

About us

What we live by

Our offices

Legal Notice

Privacy Policy

Contact

Services

Offensive Security

Managed Cyberdefense

Cyber Advisory & GRC

Training

Resources

Blog

Press Releases

Careers

Job Openings

Stroople Cybersecurity

Member of Cybermalveillance.gouv.fr, holder of the ExpertCyber label, and Qualiopi-certified for training activities.

© 2021–2026 Stroople – SAS with a share capital of €1,300,000 – 121 Rue d’Aguesseau, 92410 Boulogne-Billancourt, France – SIRET No. 92531165600019

Stroople
Close menu
  • About us
    • What we lived by
    • Our offices
  • Cybersecurity Services
    • Offensive Security
    • Managed Cyber Defense
      • External Attack Surface Management
      • Threat Exposure Management
      • Managed SOC & CERT 24/7
    • Cyber Advisory & GRC
      • CISO As A Service
      • Cyber crisis management
      • ICT Third-Party Risk Management
      • Regulatory Compliance
    • Training
      • Cybersecurity Training Programme | DORA Compliant
      • Cybersecurity Training Programme | NIS2 Compliant
      • Cyber Crisis Exercise: Immersive Training for COMEX and CIO
  • Careers
  • Resources
    • Blog
    • Cyber Talk
    • Cyber Threat Intelligence
    • Press Releases
  • Contact
    • Change language to Français